inDDoS
Corporate Assurance

Certifications & Competencies

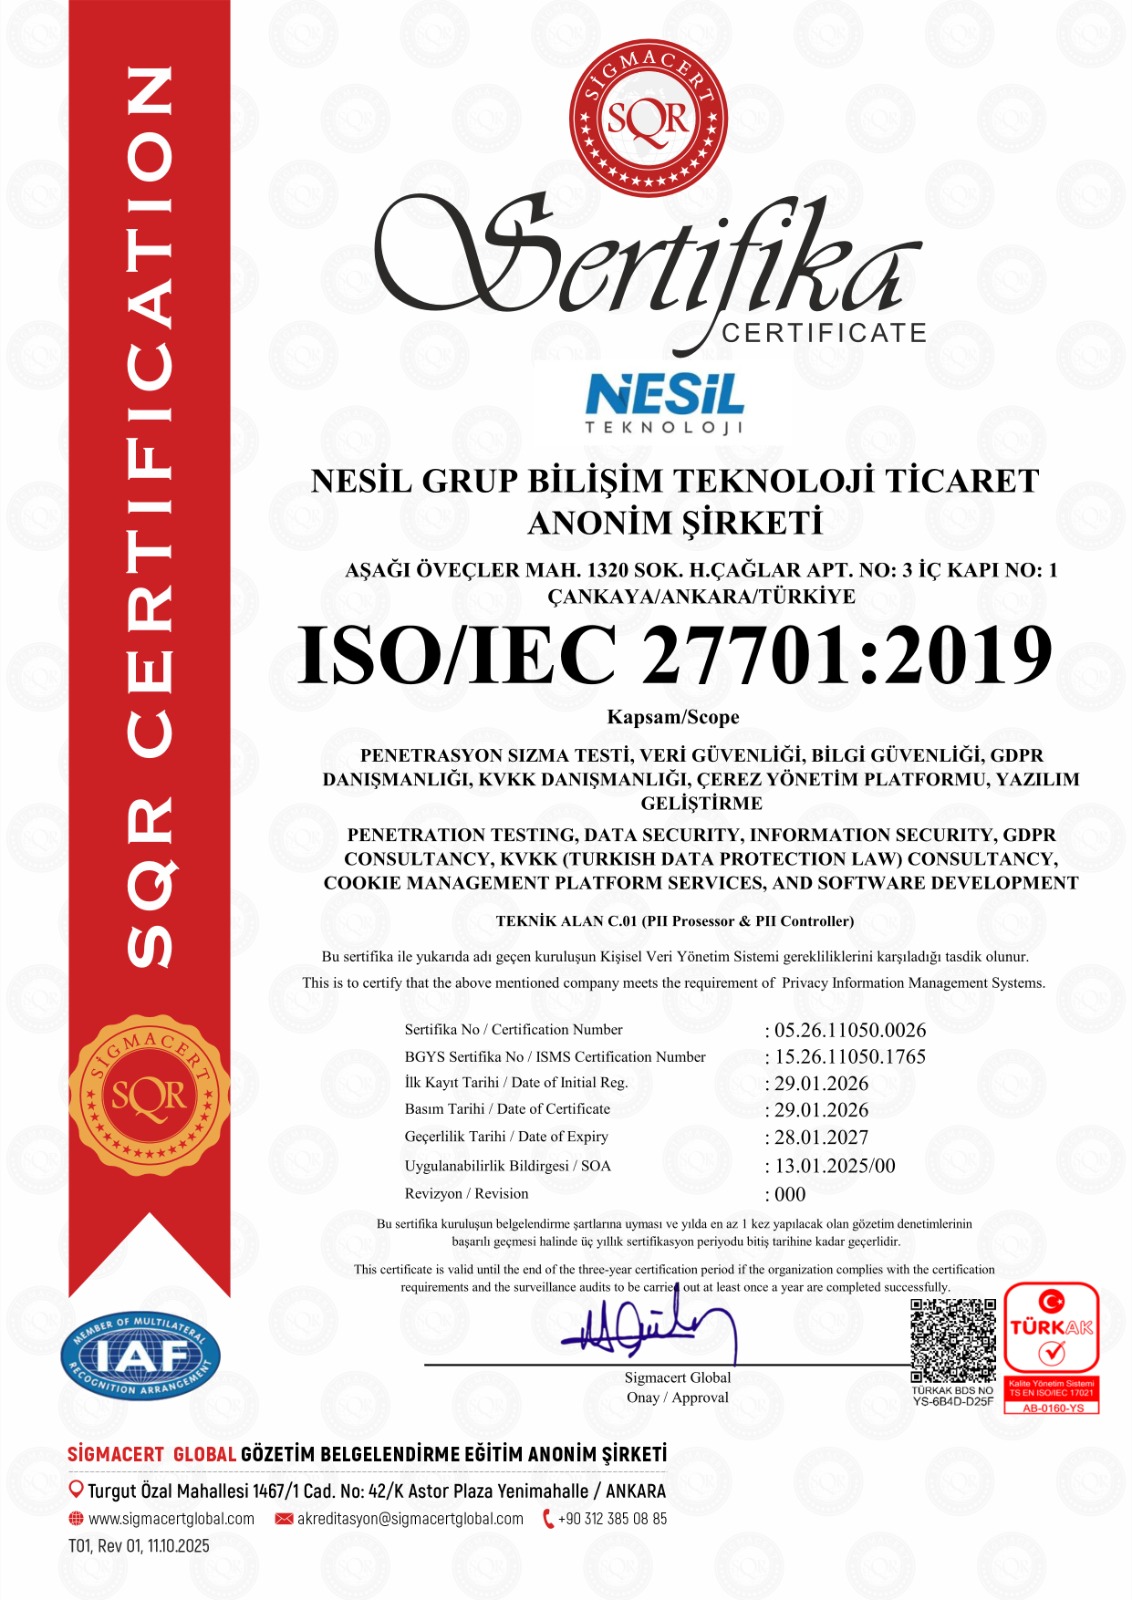
We build our penetration testing and information security services on official authorisations and on management systems audited by independent bodies. The Republic of Türkiye Ministry of Industry and Technology authorisations (STB03-250, STB01-3242), the TSE Class A Certified Penetration Testing Firm certificate (TSE-STF-065) and CREST membership work together with TÜRKAK-accredited ISO/IEC 27001:2022 and ISO/IEC 27701:2019 certificates and with ISO 9001, ISO/IEC 20000-1 and ISO 22301 management systems.

2
Ministry Authorisations
A
TSE Penetration Testing Class
5
ISO Management Systems
9
TSE-Certified Specialists

Official Authorisations & Accreditations

Ministry authorisations required in public tenders, together with our national and international penetration testing accreditations. Certificates with a number can be checked through the issuing body’s online verification system.

STB03-250

Penetration Testing Authorisation

Penetration testing services

Document details
Issued by
Republic of Türkiye Ministry of Industry and Technology
Legal basis
Regulation No. 31881

The official authorisation required to bid in public-sector penetration testing procurements.

STB01-3242

Public IT Authorisation

Public IT services

Document details
Issued by
Republic of Türkiye Ministry of Industry and Technology
Legal basis
Regulation No. 31881

Authorisation to bid in every type of public IT service procurement tender.

TSE-STF-065

TSE Class A Certified Penetration Testing Firm

Penetration Testing Firm Certificate

Document details
Standard
TS 13638
Class
Class A
Issued by
Turkish Standards Institution (TSE)

Granted to firms whose penetration testing competence is approved at the highest class following TSE audits.

SPICE-535

SPICE Level 2

Organisational Maturity Certificate

Document details
Certification body
ICT CERTIFY
Standard
TS ISO/IEC 15504-7
Maturity level
Progressive Level 2
Type / Class
A / 1
First issued
18.09.2026

Organisational maturity certificate regarding the assessment of software processes within the framework of TS ISO/IEC 15504.

Our technical team includes 9 TSE-certified penetration testing specialists, complemented by experts holding OSCP, CISSP, CISM, CISA and CIPP/E certifications and the CMB Information Systems Independent Audit License.

Accredited Management Systems & Memberships

We run our information security, privacy, quality, IT service management and business continuity processes in line with ISO standards. Our ISO/IEC 27001 and ISO/IEC 27701 certificates are issued under IAF and TÜRKAK accreditation. We also hold Member Company status within CREST International, the global benchmark for ethical security testing.

15.26.11050.1765

ISO/IEC 27001:2022

Information Security Management System

Document details
Certification body
Sigmacert Global (SQR)
Accreditation
IAF + TÜRKAK
TÜRKAK code
YS-9E73-3306
Technical area
C.01
First registered
29.01.2026
SoA
13.01.2025/00

Our Annex A controls and risk management processes undergo annual surveillance audits under TÜRKAK accreditation.

05.26.11050.0026

ISO/IEC 27701:2019

Privacy Information Management System

Document details
Certification body
Sigmacert Global (SQR)
Accreditation
IAF + TÜRKAK
TÜRKAK code
YS-6B4D-D25F
Technical area
C.01 (PII Processor & Controller)
First registered
29.01.2026
Legislation
6698 KVKK + EU 2016/679 GDPR

KVKK and GDPR compliance is assured at management-system level for processes where we act as both PII processor and controller.

CREST Membership

Member Company

Membership in CREST International, the international benchmark for penetration testing.

ScopePenetration Testing

ISO 9001:2015

Quality Management System

Measurable customer satisfaction through a risk-based approach, process-driven management and continual improvement.

ScopeCybersecurity, consulting and IT services

ISO/IEC 20000-1

IT Service Management System

Service level (SLA), incident, change and capacity management processes are defined and auditable.

ScopeSoftware development, system integration and managed security services

ISO 22301

Business Continuity Management System

Assurance that services keep running through cyber attacks, crises and operational outages.

ScopeBusiness impact analysis, recovery strategies and crisis management

Our Experts’ Certifications

Internationally recognised certifications held by our team in penetration testing, information security management and personal data protection.

TSE-Certified Penetration Testing Specialists

TS 13638 · Turkish Standards Institution
2
Senior Penetration Testing Specialist
3
Certified Penetration Testing Specialist
4
Registered Penetration Testing Specialist

Penetration Testing

Offensive Security
  • OSCP+OffSec Certified Professional PlusOffSecVerify
  • OSCPOffensive Security Certified ProfessionalOffSecVerify
  • OSEPOffSec Experienced Penetration TesterOffSec
  • OSWEOffensive Security Web ExpertOffSec
  • CRTOCertified Red Team OperatorZero-Point Security
  • CRTPCertified Red Team ProfessionalAltered Security
  • CREST CRTCREST Registered Penetration TesterCREST International
  • CREST CPSACREST Practitioner Security AnalystCREST International
  • eWPTX v2Web Application Penetration Tester eXtremeeLearnSecurity / INE
  • CEHCertified Ethical HackerEC-Council
  • LPTLicensed Penetration TesterEC-Council
  • GPENGIAC Penetration TesterSANS / GIAC

Information Security Management & Audit

ISMS & Audit
  • CISMCertified Information Security ManagerISACAVerify
  • CISACertified Information Systems AuditorISACAVerify
  • AAISM™Advanced in AI Security ManagementISACA
  • CISSPCertified Information Systems Security Professional(ISC)²
  • ISO 27001 LAISO/IEC 27001:2022 Lead AuditorSigmacert Global / Exemplar Global · Certificate No. SGM-2023-401587Open certificate
  • Security+CompTIA Security+CompTIA
  • CMBInformation Systems Independent Audit LicenseCapital Markets Board (VII-128.7) · Certificate No. 930873

Personal Data Protection & Privacy

Privacy & Data Protection
  • CIPP/ECertified Information Privacy Professional / EuropeIAPPOpen certificate
  • ISO 27701 LIISO/IEC 27701:2019 Lead ImplementerPrivacy Information Management System
  • ISO 27701 LAISO/IEC 27701:2019 Lead AuditorCFE-CERTOpen certificate
  • GDPR DPOEU GDPR Data Protection OfficerCFE-CERTOpen certificate